
This policy verifies the JSON Web token provided. If the token value has been tampered or the token is wrong, it will not allow the user to access the resource.
Configuration
The properties that have to be configured to use the policy are described below.
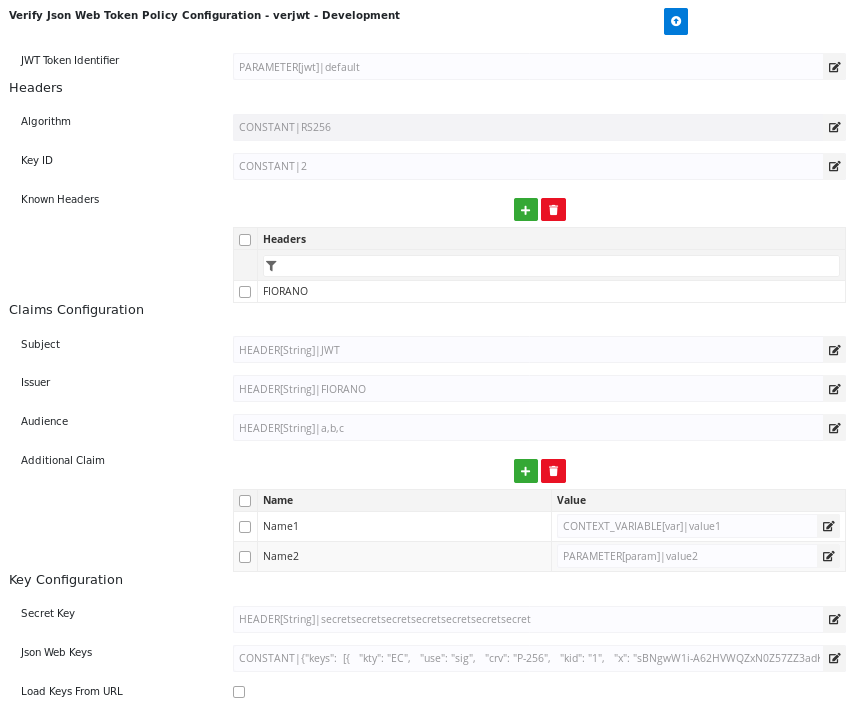
Figure 1: Verify Json Web Token policy configuration attributes
|
Property |
Description |
JWT Token Identifier
|
Configure the Message Part Identifier with the source as header/Query parameter/context variable/constant through which the JWT is passed. |
Headers
|
|
Algorithm
|
Specifies the encryption/signed algorithm which was used to encrypt/sign the JWT provided in the JWT Token Identifier property above.
Supported algorithms are HS256, HS384, HS512, RS256, RS384, RS512, PS256, PS384, PS512, ES256, ES384, ES512 , NONE.
Provide any of the above-mentioned algorithm values as input to be used to verify the token. |
Key ID
|
The Key ID value corresponding to the algorithm (specified in the Algorithm property above) as provided in the or the keys exposed in the (described below). |
|
Known Headers |
Verify JWT policy examines "crit" parameter in the JWT header, if present, and checks that each value listed under "crit" contained in JWT provided for validation is present among the entries under this "Known Headers" element i.e the "Known Headers" must contain a superset of the items listed in JWT's "crit" header. Any header that is found in "crit" header that is not specified here among <KnownHeaders> causes the policy to fail. |
Claims Configuration
|
|
Subject
|
This value should be same as that of the "sub" claim of the provided JWT for it to be valid. Provide values for Subject, Issuer, and Audience (described below) only if these values are provided in the Json Web Token policy
|
Issuer
|
The "iss" (issuer) claim identifies the entity that issues the JWT. Provide the same value as that of "iss" claim contained in the provided JWT.
|
Audience
|
The "aud" claim identifies the intended audience/recipients of the JWT. The audience value is comprised of comma separated string. Make sure this value is present among those in "aud" claim of JWT provided for successful validation. This property is optional.
|
Additional Claim
|
Source-configurable custom claims can be specified here in order to verify their values against those present in the JWT provided for validation.Make sure every claim specified here is contained in the provided JWT, otherwise it is invalidated. |
Key Configuration
|
|
Secret Key
|
Provide when a symmetric algorithm like HS256 is specified. The minimum length of the string has to be 256,384,512 bits for HS256,HS384,HS512 respectively. |
Json Web Keys
|
Provide when an asymmetric algorithm like RS256 or ES256 is specified. A sample is as shown below:
For the JWK structure as in the sample above, refer to the link: https://tools.ietf.org/html/rfc7517.
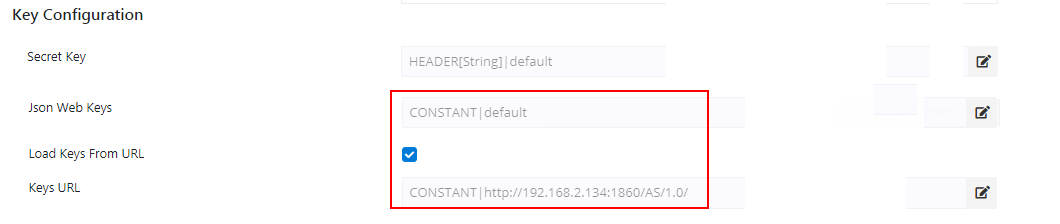
Alternatively, the Public Json Web Keys can be provided in the following ways:
|
Load Keys From URL
|
If Public Json Web Keys are exposed in a specific URL, then enable this property. |
Keys URL
|
Specify the URL in which Public Json Web Keys are exposed. |
Verifying a Json Web Token
Request
Use the following URL in the browser/postman:
http://192.168.2.231:2160/jsonVerifytoken/1.0?jwt-token=ewogICJ0eXBlIiA6ICJKV1QiLAogICJhbGciIDogIkhTMjU2IiwKICAia0lEIiA6ICIxMjM0NTYiCn0=.ewogICJzdWIiIDogIkpzb24tVG9rZW4tR2VuZXJhdGlvbiIsCiAgImlzcyIgOiAiRmlvcmFubyBzb2Z0d2FyZSBwcml2YXRlIGx0ZC4iLAogICJhdWQiIDogImF1ZGllbmNlIiwKICAiaWF0IiA6ICIyMDE4LTA5LTExIDIyOjM1OjEwIiwKICAiZXhwIiA6ICIyMDE4LTA5LTE1IDIyOjM1OjEwIiwKICAic2hvdyIgOiAiZmlvcmFubyIsCiAgImFkZGl0aW9uYWxDbGFpbSIgOiB7IH0KfQ==.n8YbWfgmw9v/4iYOnC7G2qFLhzUf3jVgQHUK8oWn7qg=
Response
Attains access of the resources if the token is valid.