
This policy verifies the generated JWS. If the signature value has been tampered or the signature is different, it will not allow the user to access the resource.
Configuration
The properties that have to be configured to use the policy are described below.
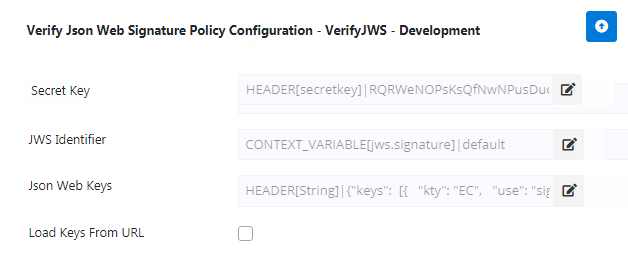
Figure 1: Verify Json Web Signature Policy configuration attributes
|
Property |
Description |
Secret Key
|
Provide when a symmetric algorithm like HS256 is specified. The minimum length of the string has to be 256, 384, 512 bits for HS256, HS384, HS512 respectively. |
JWS Identifier
|
Configure the Message Part Identifier with the source as header/Query parameter/context variable/constant through which the JWT is passed. |
Json Web Keys
|
Provide when an asymmetric algorithm like RS256 or ES256 is specified. Please refer to the Json Web Keys property description in the Verify Json Web Token policy to know how to input the Public JSON Web keys.
|
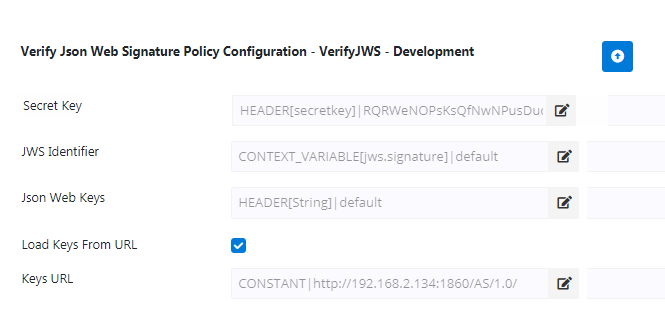
Load Keys From URL
|
If Json Web Keys are exposed in a specific URL, then enable this property. |
Keys URL
|
Specify the URL in which Json Web Keys are exposed. |
Detached Content
In certain cases, it will be useful to protect the integrity of the content that is not itself contained in a JWS. Perform the following actions by detaching content as follows:
-
Create Assign Variable policy with the respective variable names and identifiers.
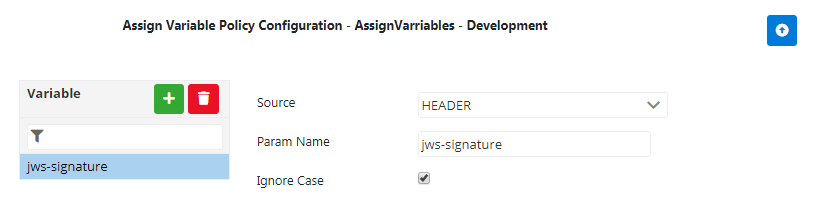
Figure 2: Verify Json Web Signature Policy configuration attributesThis sets the values in context variable with the specified names.
-
Go to $FioranoHome/APIManagement\samples\JavaCallOuts\DetachedJWSClaim and run the compiled script. This creates a Classes directory containing a jar with compiled classes.
The java class can be modified as per requirement.
-
Configure Java Callout policy using the jar created above.
-
Configure the Verify JWS policy as explained in this page.
Verifying a Json Web Signature
Request
Use browser/postman to send the request as below:
curl -X POST \http://192.168.2.231:2160/verifycustomgignature/1.0/ \-H 'jws-signature:ewogICJ0eXBlIiA6ICJKV1QiLAogICJhbGciIDogIkhTMjU2IiwKICAia0lEIiA6ICIxMjM0NTYiCn0=.ewogICJzdWIiIDogIkpzb24tVG9rZW4tR2VuZXJhdGlvbiIsCiAgImlzcyIgOiAiRmlvcmFubyBzb2Z0d2FyZSBwcml2YXRlIGx0ZC4iLAogICJhdWQiIDogImF1ZGllbmNlIiwKICAiaWF0IiA6ICIyMDE4LTA5LTExIDIyOjM1OjEwIiwKICAiZXhwIiA6ICIyMDE4LTA5LTE1IDIyOjM1OjEwIiwKICAic2hvdyIgOiAiZmlvcmFubyIsCiAgImFkZGl0aW9uYWxDbGFpbSIgOiB7IH0KfQ==.n8YbWfgmw9v/4iYOnC7G2qFLhzUf3jVgQHUK8oWn7qg=' \-d '{"iss":"fiorano"}'
Response
Verifies the signature and allows to access the respective resources.